Cognizant will use the full Qualys portfolio to bring its clients what the frontier AI era demands: AI-speed detection, hyper-prioritization, and confident remediation for every zero-day.
When a critical zero-day goes public, security leaders ask two questions: which assets are affected, and how fast can we safely fix them? For most enterprises, the current answer is days, then weeks.
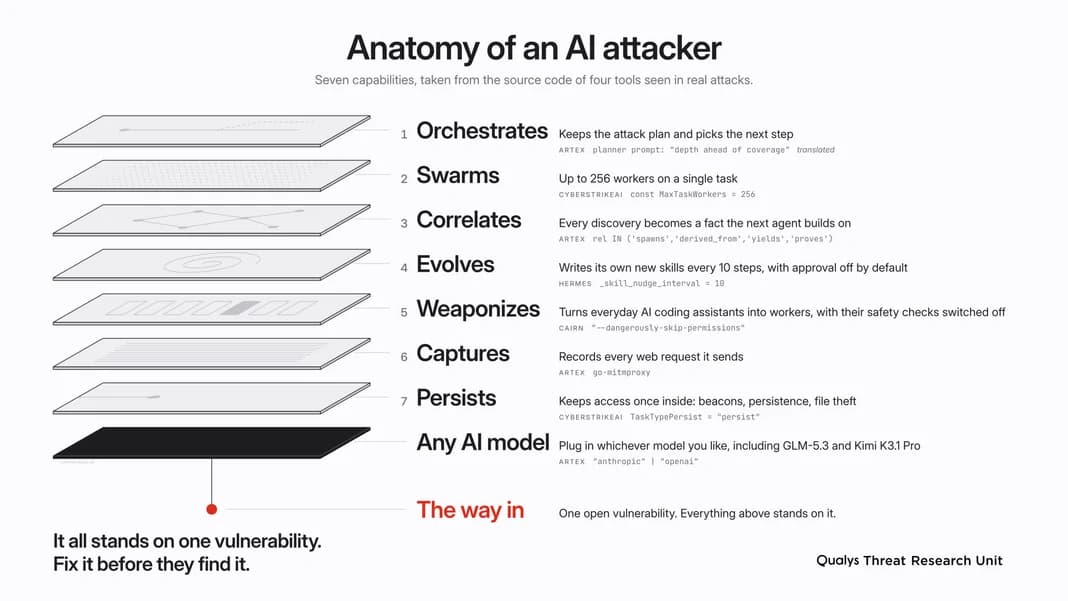
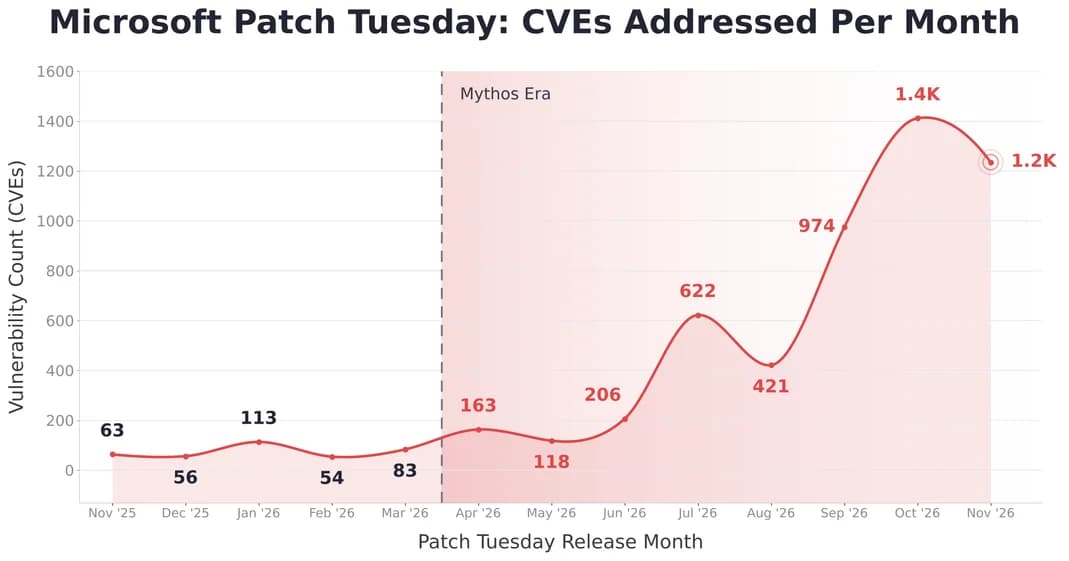
Frontier AI makes that remediation timeframe dangerous. Microsoft’s November Patch Tuesday alone carried 1,093 vulnerabilities, up from 93 in November 2025 before frontier AI models arrived. AI-assisted attackers can weaponize a new advisory in four to twelve hours, while scan-driven detection often takes 24 to 36 hours just to show which assets are affected. The risk is already real: Cognizant’s 2026 Cybersecurity Pulse Poll found that 83% of participating U.S. enterprises had an AI-related security incident in the past 24 months.
Knowing what to fix is only half the gap. Every step from finding to fix is still gated by people, for one reason: fear that a patch will break production, that a reboot will take down a critical system, or that there is no fast way back. Teams will not hand fixes to automation they do not trust.
Cognizant helps the world’s largest enterprises scale with AI, through its AI Builder approach, and recognizes that its clients need security that moves at machine speed. Already running managed services on Qualys ETM, Cognizant is now expanding to the full Qualys portfolio, including TruRisk Eliminate. That is why I am excited to welcome Cognizant to the Qualys Global mROC Alliance.
Managed detection is table stakes. This is the dawn of the 24-hour autonomous remediation service, run from Qualys ETM: a zero-day disclosed, detected, prioritized, and remediated within a day.
Why the Qualys Platform Fits Cognizant’s Approach
Running zero-day response as a service, at enterprise scale, puts specific demands on the platform underneath. Cognizant needed three capabilities working as one:
- One record for every asset, across every tool, built from Qualys and non-Qualys sources, so there is no reconciling data across disparate tools before anyone can act.
- Exploit validation in each client’s own environment, so every hour of the client’s team’s time goes to risk that is real.
- Remediation with confidence, so automation can be trusted within production systems.
Qualys delivers all three on one platform, with the agentic AI to run them at machine speed.
Cognizant brings what a platform alone cannot: Cyber Vulnerability Management services and threat intelligence, delivery experience inside large enterprises, and a view of risk in financial terms for the board. Its operators run the Risk Operations Center, powered by Qualys ETM to navigate inside each client’s own tools, change windows, and approvals. Clients keep control of what gets fixed and when. Cognizant carries the daily work.
“Our 2026 Cybersecurity Pulse Poll shows that strength in one control, such as detection or remediation, still leaves enterprises exposed in the AI era. Together with Qualys, we are connecting detection, prioritization and remediation into one managed operating model, helping clients reduce risk, strengthen resilience and scale AI with confidence.” — Vishal Salvi, SVP and Global Head of Cybersecurity, Cognizant
“Our 2026 Cybersecurity Pulse Poll shows that strength in one control, such as detection or remediation, still leaves enterprises exposed in the AI era. Together with Qualys, we are connecting detection, prioritization and remediation into one managed operating model, helping clients reduce risk, strengthen resilience and scale AI with confidence.” — Vishal Salvi, SVP and Global Head of Cybersecurity, Cognizant
Cognizant will deliver four mROC services on the Qualys platform:
- Cyber risk quantification and advisory services. Cyber risk for business applications shown in dollars, with a personalized risk plan and a report for the board.
- Onboarding and integration. The security tools a customer already owns connected into one record for each asset, with data quality checked from day one.
- Risk monitoring as a managed service. AI-speed alerts on new CVEs, a validated queue instead of noise, and a weekly exposure review, using InstaScan, Agent Val, and ROCky.
Risk remediation as a managed service. A wave-based plan built from the Risk Elimination Playbook, zero-touch remediation where it is safe, and proof the fix held, using TruRisk Eliminate, TruConfidence, and Agent Sara.
AI-Speed Detection: Every Exposure Known in Minutes
Frontier AI has changed the rhythm of disclosure. Vulnerabilities now land in volume, and attackers act on them in hours, well inside any scan cycle.
Qualys InstaScan, delivered by Agent Insta, closes that gap. It turns the inventory and telemetry a client already has, from Qualys and non-Qualys sources, into high-confidence findings within minutes of disclosure. No new scan, no new agent.
On November’s Patch Tuesday, InstaScan delivered 90% of detections within minutes. The first landed about 40 minutes before Microsoft’s own release notes went live. With Cognizant, that speed turns into action. Through its risk monitoring service, Cognizant analysts watch for new disclosures every day, confirm each exposure, and route it to the right asset owner with context. The client’s team no longer chases owners or rebuilds asset lists every time a new CVE trends.
Hyper-Prioritization: Proven Exploitability
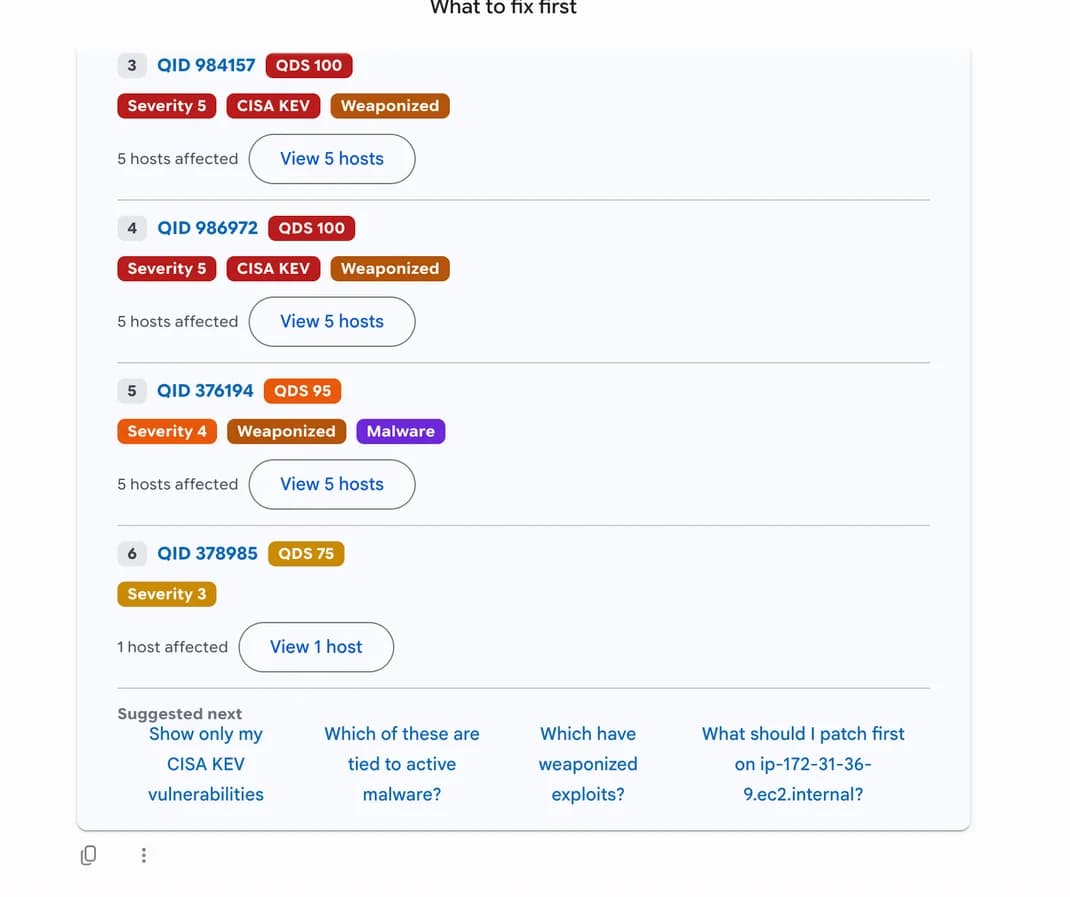
More vulnerabilities do not mean more risk. Of the 48,172 vulnerabilities disclosed in 2025, the Qualys Threat Research Unit found only 357 (0.74%) confirmed remotely exploitable and actively weaponized. No team can work the full list, and none should have to.
Agent Val and TruConfirm test what is actually exploitable in the client’s own environment, with existing controls counted. Critical on paper but blocked by a control? It leaves the urgent queue. Exploitable on a PCI-scoped server? It goes to the top.
Cyber Risk Quantification (CRQ) then puts validated risk in dollars, by business application, so the CISO can show the board what each fix is worth.
With Cognizant, the short list becomes a working rhythm. Through its risk monitoring and advisory services, Cognizant keeps each client’s validated queue current and reviews it with them every week. The client’s team stops triaging noise and starts each week knowing exactly what to fix first.
Autonomous Remediation: Remediate with Confidence and Maintain Operational Resiliency
That fear is why the global mean time to remediate sits at about 30 days. TruRisk Eliminate, with TruConfidence, removes it by protecting operational resiliency before, during, and after every change.
- Before: TruRisk Eliminate chooses the safest fix for each finding: patch, mitigate, isolate, or uninstall. A patch reliability score decides what deploys automatically and what goes ring by ring.
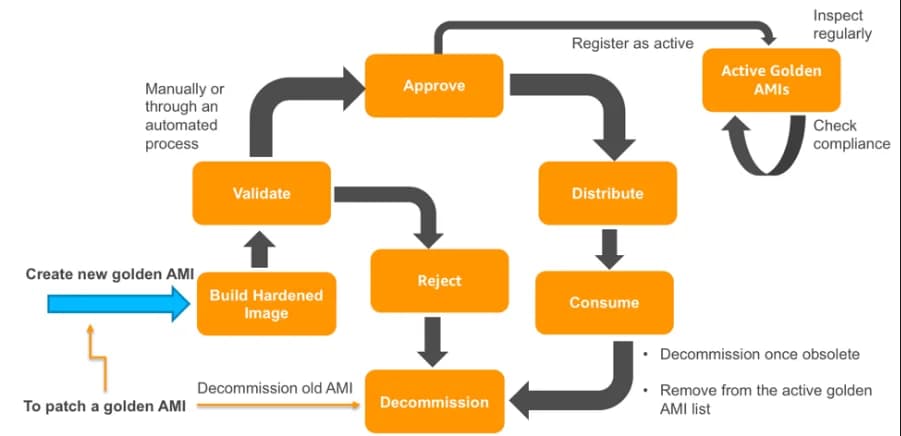
- During: Changes roll out in waves, starting with low-risk rings. System health is watched through each wave, and rollback restores a known-good state if health drops.
- After: AI-powered patch failure analysis pinpoints why a change failed and the corrective actions, and automated rollback restores a known-good state.
Showing clients the 1% that matters
Cognizant can open every client engagement with a Risk Elimination Playbook, powered by TruConfidence and built for that client’s environment. It narrows the backlog to the 1% that must be fixed now and moves the rest into planned software updates. It also benchmarks the client’s mean time to remediate against peers, and shows how much of the backlog autonomous remediation can close, and how much faster.
It becomes the plan behind every remediation wave and the baseline for every review.
Where Managed Security Goes Next
The three pillars together provide a new kind of service: 24-hour autonomous remediation, run from ETM. Cognizant can take a critical zero-day from disclosure to remediation within a day, for every client, with operational resiliency built in at every step.
Managed security is moving from raising alerts to closing risk. Cognizant is among the first to deliver that at enterprise scale, and I expect it to set the bar enterprises hold every provider to. That is what the Global mROC Alliance was built for: the platform, the certification path, and the operating model to run the Risk Operations Center as a service.
Attackers already move at AI speed. This expanded partnership helps tip the balance back toward the defense.
To learn more, visit the Qualys Global mROC Alliance page, read the press release, or contact your Cognizant or Qualys account team.