Checkmarx and OpenAI are bringing application security findings into OpenAI Daybreak Defense Factory, connecting trusted vulnerability detection with AI-powered investigation and remediation.
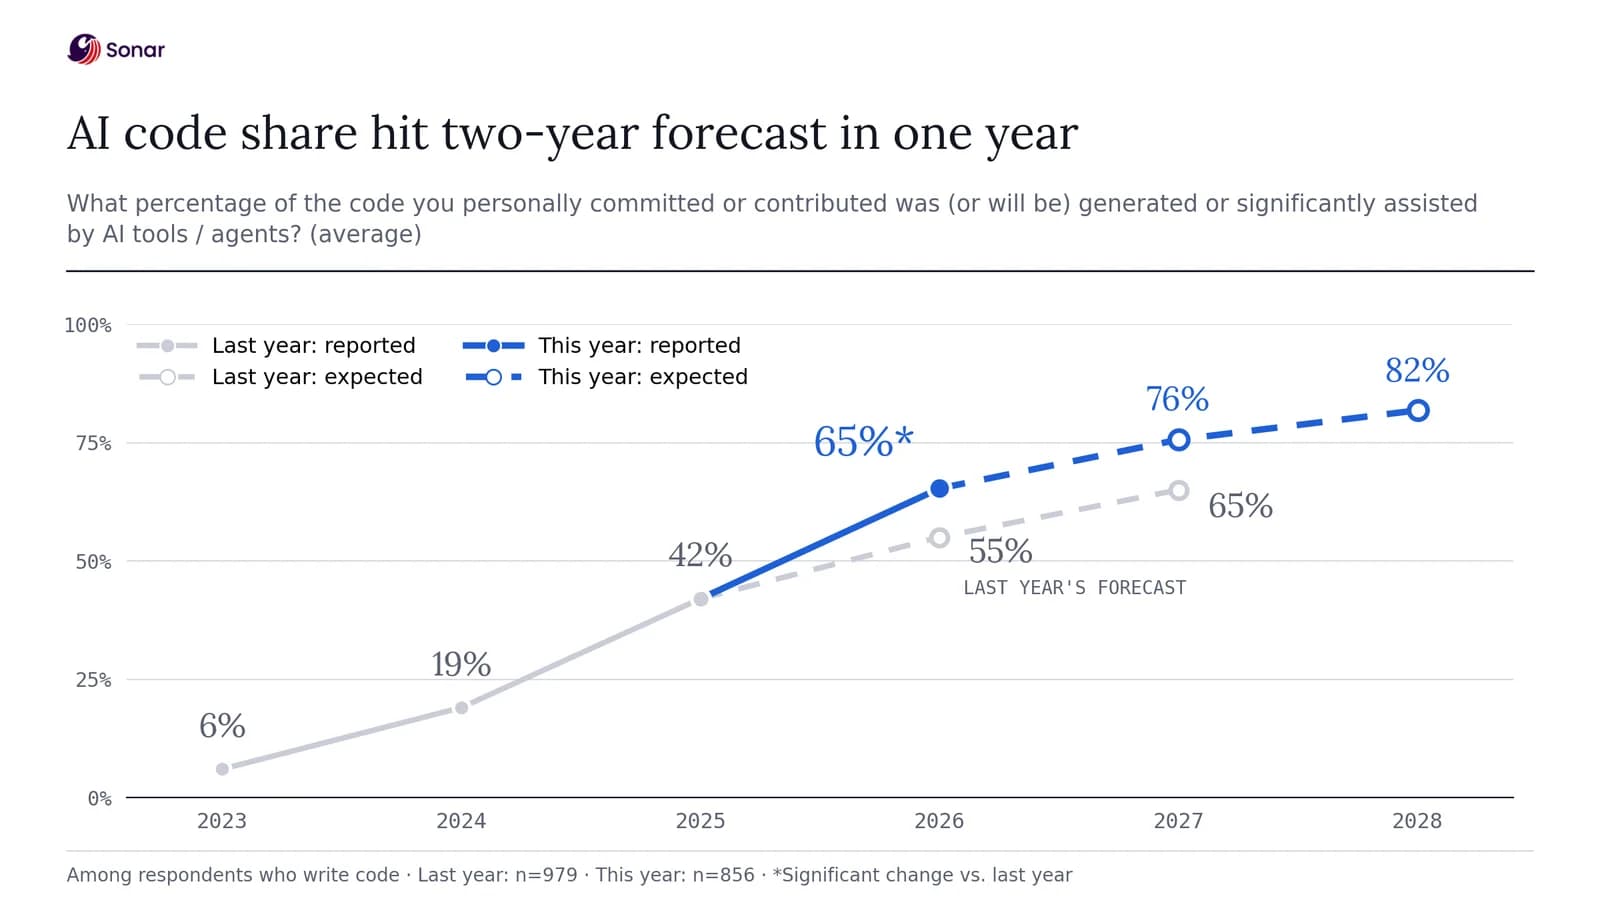
AI is fundamentally changing how software gets built. Developers can generate, modify and ship code faster than ever. But more code also means more opportunities for vulnerabilities, creating an increasingly difficult backlog for security teams to manage.
Finding vulnerabilities is only part of the problem. Investigating findings, understanding their impact, determining the right remediation and validating fixes all take time. As AI accelerates development, the volume of vulnerabilities can grow faster than teams’ ability to address them.
That’s the challenge Checkmarx and OpenAI are working together to solve.
Through a new integration, organizations can bring Checkmarx findings into OpenAI Daybreak Defense Factory, connecting established application security analysis with a frontier lab platform.
Checkmarx recognized the challenge early
At Checkmarx, we recognized that finding more vulnerabilities wouldn’t solve the growing application security challenge if organizations couldn’t keep up with remediation. Addressing this gap requires more than better detection; it requires helping security teams prioritize, investigate and resolve vulnerabilities more effectively.
This is why we were the first to launch dedicated agents for triage and remediation – Triage Assist and Remediation Assist, now generally available in Checkmarx One. These capabilities help security teams prioritize vulnerabilities and give developers the context and proposed fixes needed to address them.
But this is bigger than any one company or product. As organizations adopt AI-powered development tools, application security must evolve alongside them. Solving the growing vulnerability backlog requires technology leaders across the industry to work together.
That’s why we’re working with OpenAI.
By bringing Checkmarx SAST findings into Daybreak Defense Factory, we’re extending established application security intelligence into another agentic security environment and helping organizations put their existing security investments to work.
From finding to fix
Checkmarx provides the security analysis and supporting evidence that developers can directly import into Daybreak Defense Factory to prepare proposed fixes for developer review.
For example, a Checkmarx SAST scan might identify a potential SQL injection vulnerability in an application. Rather than requiring a developer to manually retrace the vulnerable code path and reconstruct the issue, the team can import the finding and its supporting evidence into Daybreak Defense Factory.
Daybreak Defense Factory can investigate the affected code and, if remediation is warranted, propose a targeted correction, such as replacing unsafe SQL construction with parameterized queries.
The developer reviews the proposed change, tests it and approves the fix. A follow-up Checkmarx scan can help verify that the original vulnerability has been addressed.
The agent proposes. The developer decides.
How to get started
Security teams can get started using an existing, completed Checkmarx SAST scan. The integration supports both Checkmarx One and self-managed CxSAST deployments.
The process involves:
- Confirming access: Ensure the team has access to Daybreak Defense Factory and that the deployment accepts the Checkmarx provider.
- Preparing scan results: Use a completed Checkmarx One or CxSAST scan. Supported formats include Checkmarx One JSON and CxSAST XML reports.
- Previewing and importing: Preview the findings selected for import by running the Codex Security CLI with the –provider checkmarx and –dry-run options, then run the same command without –dry-run to import them.
- Reviewing and remediating: Let Daybreak Defense Factory investigate findings and help prepare proposed fixes. Developers review, test and approve changes before a follow-up Checkmarx scan.
For detailed setup instructions, authentication requirements and supported options, consult the Checkmarx integration guide in OpenAI’s Codex Security repository.
Building a more effective path to remediation
Organizations shouldn’t have to replace the application security tools they trust to take advantage of agentic AI.
Checkmarx continues to invest in detecting, prioritizing and remediating vulnerabilities through Fusion SAST, Triage Assist and Remediation Assist. Our work with OpenAI extends that commitment by making Checkmarx security intelligence available within another agentic security environment.AI is accelerating software development, and keeping applications secure will require collaboration, stronger detection and more effective remediation workflows.
Ultimately, application security isn’t measured by how many vulnerabilities we find. It’s measured by how effectively we help teams fix them.