Building an AI agent takes more than a model.
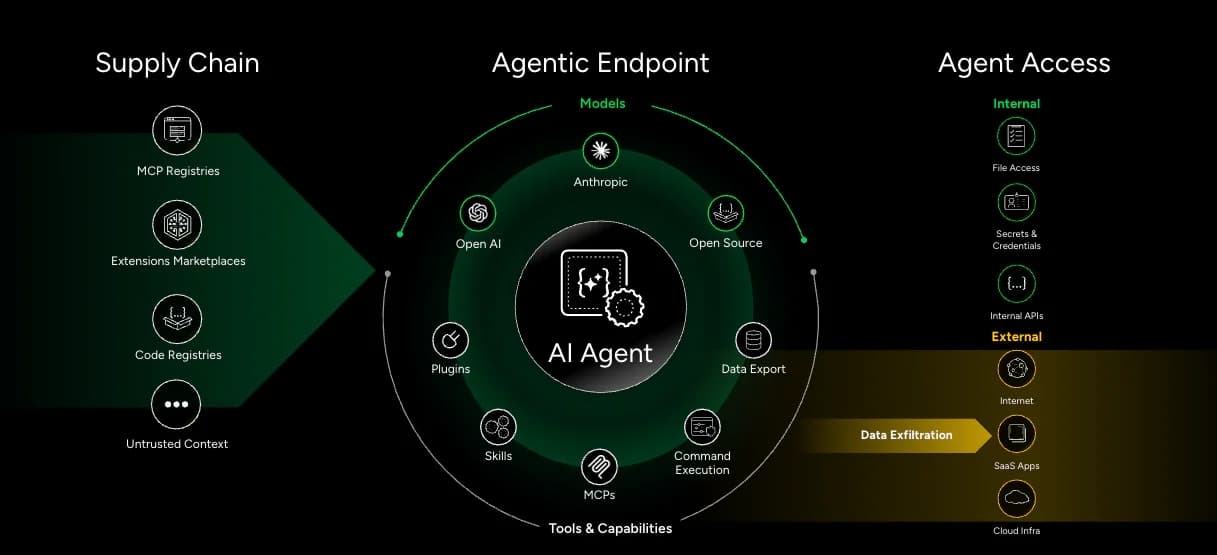
An agent might retrieve sensitive information from a knowledge base, authenticate through a service identity, or connect to external tools to complete a task. Each interaction depends on resources with their own permissions, configurations, and potential security risks.
Cloud providers are expanding their AI offerings beyond model development, introducing managed agent platforms and infrastructure that make it easier to build, deploy, and scale AI applications. But as these environments grow, so do the potential points of exposure.
For security teams, knowing which AI models are running is no longer enough. They also need to understand what agents can access, how supporting infrastructure is configured, and where security risks may emerge across the AI ecosystem.
But as developers spin up new agents, workspaces, and services, how much of that infrastructure can security teams actually see? An overlooked configuration or overprivileged identity could expose sensitive data long before anyone realizes there's a problem.
The Expanding AI Ecosystem Introduces New Security Challenges
A cloud inventory might show a compute instance, storage bucket, or service identity. But can it tell you which AI agents are running, what data they can access, or how their supporting infrastructure is configured?
Traditional cloud security tools can identify the underlying resources, but often lack the context to recognize agent runtimes, model endpoints, and development workspaces as distinct AI assets.
An agent operating with excessive permissions could access resources beyond its intended scope. A misconfigured notebook could expose sensitive data. Even when the underlying infrastructure is monitored, these risks can go unnoticed without visibility into the AI applications and services running on it.
Securing the AI ecosystem starts with bringing its hidden infrastructure and potential exposures into view.
What’s New: Unified AI Security Across AWS and Google Cloud
Cortex Cloud is closing the visibility gap in the managed AI ecosystem. With the release of Cortex Cloud 2.3, we are extending AI Security Posture Management (AI-SPM) to the core infrastructure layers where enterprise agents live and breathe.
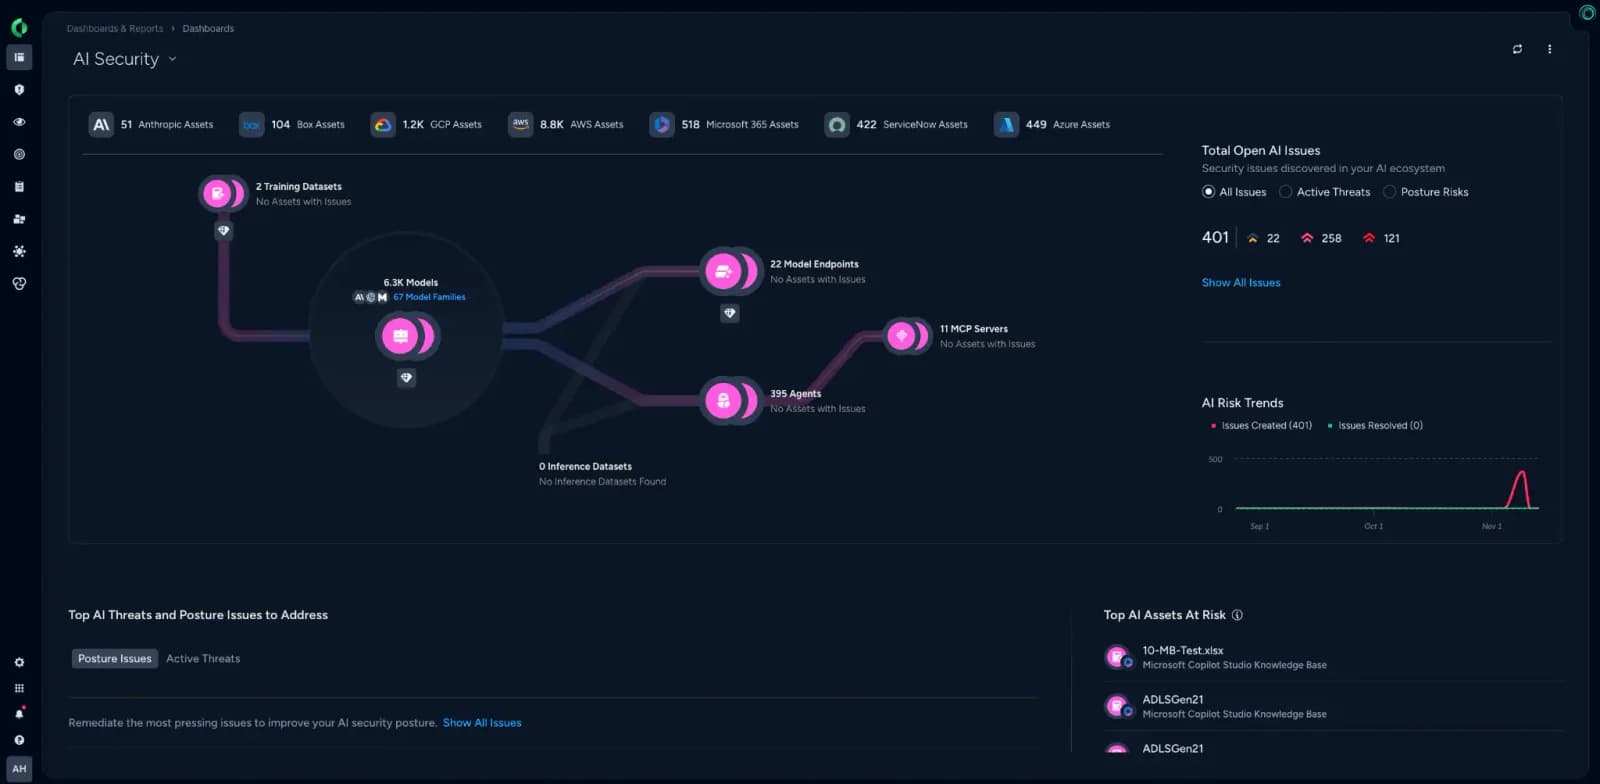
Security teams can now achieve a complete AI Bill of Materials (AI-BOM) across their multi-cloud environments, mapping the entire lineage of an agent - from the underlying foundation models and datasets to the active runtimes and connected tools.
Key Capabilities in this Release:
- Expanded Visibility for AWS Bedrock AgentCore: Automatically discover and secure the managed infrastructure supporting your AWS agents, including Agent Runtimes, Gateways and Agent Tools.
- Deep Security for GCP Gemini Enterprise Agent Platform: Gain granular insights into Agent Identities and Credentials, Gateways and MCP Servers to ensure fine-grained access control and data governance.
- Inactive Agent & Endpoint Detection: Identify stale or experimental agents and model endpoints that are no longer in use, allowing you to proactively reduce your attack surface and eliminate "AI Sprawl."
- Enhanced SageMaker Support: Extended discovery for SageMaker Domains, Spaces, and Notebooks, securing the AI development lifecycle long before models reach production.
Build a More Complete Picture of AI Security Risk
As organizations expand their use of AI across AWS and Google Cloud, securing these environments requires visibility beyond models and agents alone.
With expanded AI-SPM coverage in Cortex Cloud 2.3, security teams can discover the infrastructure, identities, and connected resources supporting their AI applications, identify risky configurations, and better understand potential exposures across their environments.
By bringing these assets together in a unified AI Bill of Materials (AI-BOM), Cortex Cloud helps organizations identify and address security risks as their AI environments continue to evolve.
See Cortex Cloud AI Security in Action
Want to see how Cortex Cloud uncovers security risks across your AI ecosystem?Request a demo to explore AI asset discovery, risk detection, and security posture management across AWS and Google Cloud.