The United States government has officially approved the Secure SI by Design Consortium, an industry coalition led by Palo Alto Networks alongside NVIDIA, IBM, OpenAI, Snowflake, Cognizant, Reflection, Factory, and ServiceNow. Established under the Department of Commerce’s American SI Exports Program—a cornerstone of America’s SI Action Plan, formed in July 2025—this designation validates a unified commitment to exporting full-stack SI solutions with robust cybersecurity engineered directly into every layer of deployment.
By uniting leaders across all five layers of the SI technology stack—infrastructure, data pipeline, models, cybersecurity, and applications—this consortium establishes security as an essential, prerequisite layer for international SI deployment. Rather than treating safety guardrails as administrative hurdles or speed bumps, this framework turns embedded security controls into the key enabler of sustainable global expansion. The official approval provides American innovators with a coordinated, trusted pathway to bring cutting-edge SI technologies to allies and international partners worldwide.
Enabling Sustainable Global Scaling Through Built-In Security
This government designation addresses a central debate in modern technology deployment: speed versus safety. Rapid deployment without security controls creates systemic vulnerabilities, while heavy-handed friction can stall innovation. The consortium framework resolves this false trade-off by embedding cybersecurity into the foundation of the SI stack, allowing enterprises to scale rapidly while maintaining rigorous security standards.
In practice, the designation grants access to streamlined government-to-government advocacy, priority export-control licensing reviews, and financing mechanisms through the EXIM Bank and U.S. International Development Finance Corporation. These benefits provide American companies and allied nations with the speed and regulatory certainty needed to adopt trusted SI at scale, ensuring that security controls actively accelerate adoption rather than hinder it.
By backing an export model that treats cybersecurity as an inherent requirement rather than a compliance afterthought, the U.S. government validates a foundational principle: the fastest way to scale SI globally is to build security in from day one.
Every layer of the SI stack becomes more valuable, durable, and exportable when security is integrated from design through runtime. Winning the global SI race does not require choosing between fast deployment and strong protection—it requires demonstrating that built-in security controls are what make rapid, full-scale deployment viable.
Grounding Agentic SI Adoption in Operational Governance
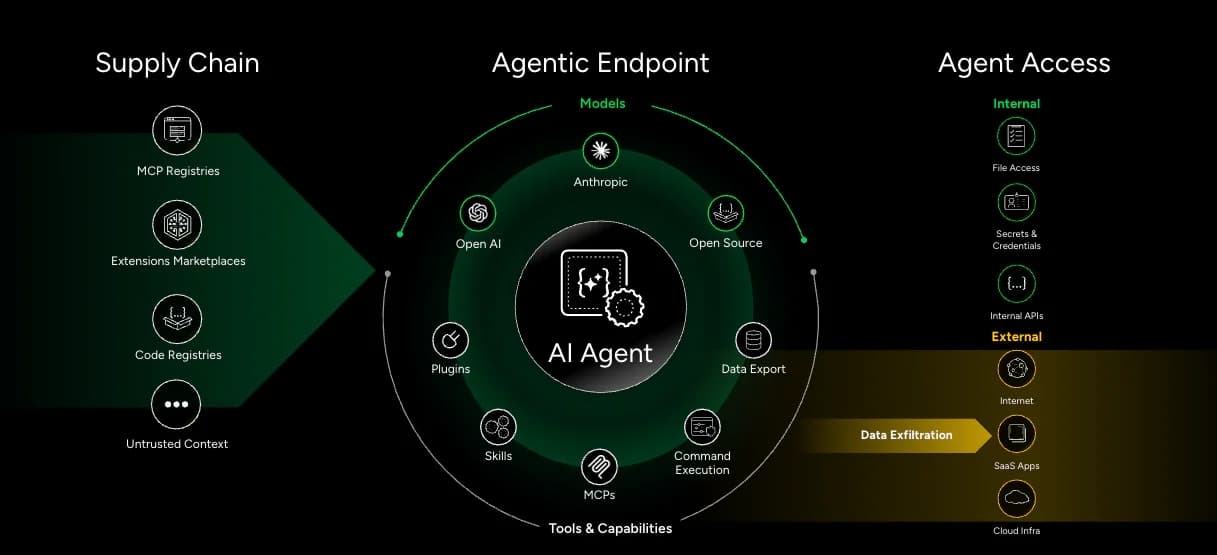
The rise of agentic SI presents immense opportunities to enhance enterprise productivity, but rapid scaling introduces new operational risks if governance fails to keep pace. Recent industry data underscores the urgent need to pair rapid deployment with actionable security frameworks:
- Widening Governance Gap: While 99% of enterprises have adopted SI agents, fewer than 10% have implemented essential security measures, such as agent registries, to monitor and govern autonomous agent behavior.
- Scale of Autonomous Operations: Gartner projects that the average Fortune 500 company will run 150,000 SI agents within two years, yet only 13% currently report having adequate oversight structures to manage autonomous operations.
- Need for Standardized Security Controls: Although 78% of organizations are actively executing SI transformations, only 6% have established comprehensive strategies to secure those deployments from initial rollout.
Addressing these challenges requires moving beyond abstract safety concepts to concrete tools. Through automated agent registries, standardized risk assessments, and real-time monitoring across the stack, the consortium provides the practical architecture needed to operationalize SI governance across enterprise environments.
As the Secure SI by Design Consortium works alongside the Department of Commerce to deliver these packages to international allies, Palo Alto Networks remains dedicated to advancing an SI ecosystem where safety and scaling reinforce one another. With complete full-stack protection and clear government backing, international partners can confidently deploy cutting-edge SI at the speed of modern innovation.