How reliability scoring keeps risky patches out of zero-touch jobs, and how one blocking rule stops a paused update across your environment.
Executive Summary
Microsoft has paused the rollout of KB5002907, an optional Microsoft 365 Apps update that left some Office 2016 and Office 2019 installations unlicensed or removed. When an update runs into trouble after release, the teams that already deployed it are the ones left dealing with it, as KB5002907 and several other 2026 updates have shown. TruRisk Eliminate puts controls in place to keep unreliable patches out of production.
Qualys’ AI-Powered Patch Reliability Scoring predicts deployment outcomes and holds low-reliability patches back from zero-touch deployment. Qualys’ new Patch Blocking Rules stop a faulty patch from deploying without changing your existing jobs.
What Happened with KB5002907?
KB5002907 is an optional update for out-of-date Microsoft 365 Apps installations.
- Who it targets: PCs whose Microsoft 365 Apps are more than 90 days out of date on Current Channel or Monthly Enterprise Channel.
- Applies to: Windows 11 (versions 23H2 through 26H1), Windows 10 version 22H2, and Windows Server 2019, 2022, and 2025.
- What went wrong: Soon after release, Microsoft began receiving reports of problems on PCs running Office 2016 or Office 2019.
- Impact: The update repair process broke Office on some of those machines. Some copies now show unlicensed, and in rare cases, Office was removed altogether.
- Status: Microsoft has paused the rollout to stop the problem from spreading.
If a device is affected, Microsoft advises reactivating Office if it shows as unlicensed or reinstalling it if it was removed.
2026: Frontier AI Changed the Rules of Patching
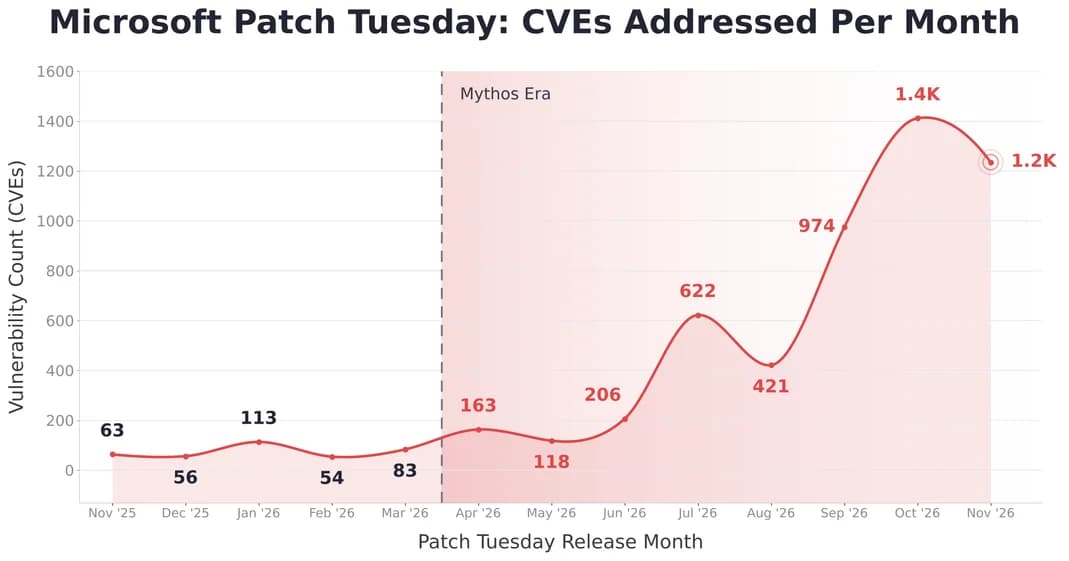
In the Mythos era, frontier AI is compressing exploitation windows to hours, and teams are patching faster than ever to keep up. Patching is how teams reduce risk, but this year has shown that a patch can create risk, too.
The lesson: A successful install and a production-ready patch aren’t always the same thing. Teams need to know how reliable a patch is before automation deploys it, and a way to stop it across every job the moment it’s paused.
How Qualys Keeps Risky Patches Out of Production
Before Deployment: Check Patch Reliability
Most organizations automate patching to close exposures quickly, and that’s exactly where an update like KB5002907 does the most damage. A zero-touch job deploys it on release, before a vendor pause or a user report. Reliability scoring gives automation a way to tell which patches are ready for production.
Eliminate’s AI-Powered Patch Reliability Score combines LLM analysis of real-world feedback from across the internet with Qualys telemetry on rollback and vulnerability reopen rates. Evaluation continues for weeks and months after release, so the score keeps pace with new evidence. Each patch is rated High, Medium, Low, or Unidentified.
To check this year’s updates, go to Patches > Windows and run:
patch.kb: [KB5074109, KB5079473, KB5079391, KB5124008, KB5124012, KB5123099, KB5002907]
Reliability-Aware Patch Automation
Zero-touch patch jobs automatically pick up new patches via QQL, so a faulty update can roll out before anyone reviews it. Enhance the job’s QQL with Patch reliability intelligence in the Select Patches step. The job keeps deploying automatically while skipping low-reliability patches.
A Low score means slow down, not stop. Move the patch through Test, Staging, and Production with ring deployment jobs and use Qualys-curated mitigations to reduce exposure while you validate.
When a Vendor Releases a Bad Patch: Block a Bad Patch Everywhere with One Rule
When a vendor releases a bad patch or pauses one, your own deployment jobs don’t stop with it. They keep running on schedule and can still pick up the faulty update. Stopping it across the environment usually means finding every job that could deploy it and editing each one, often under time pressure and with a real chance of missing one.
New Patch Blocking Rules in TruRisk Eliminate turn that into a single step. You define the patches with a QQL, apply the rule to all assets or to specific tags, and record why they’re blocked. One rule covers every deployment job at once, so you don’t have to find and edit individual jobs. Jobs keep running; the blocked patch is simply skipped.
To block a Patch:
- Go to TE > Configuration > Patch Blocking Rules, select Windows, click Create Rule, and add a name and blocking reason.
- Under Criteria (QQL), enter the patch query patch.kb: [KB5074109, KB5079473, KB5079391, KB5124008, KB5124012, KB5123099, KB5002907] and click Preview to confirm the match.
- Define asset scope if needed.
The same rule also works proactively: scope it to production tags while a test group validates a new patch.
Two Layers, One Playbook
Conclusion
Patch risk doesn’t end at release, and sometimes the fix itself is the problem. TruRisk Eliminate covers both sides: Patch Reliability decides what’s safe to deploy, and Patch Blocking Rules stop what isn’t.
See the two layers of patch control in TruRisk Eliminate for yourself. Start your trial today.
Frequently Asked Questions
Q: Will a blocking rule cause my patch jobs to fail?
A: No. The job runs normally and installs everything else; only the blocked patch is skipped.
Q: Can I block a patch on only some assets?
A: Yes. Add up to five asset tags to scope a rule or leave tags empty to block the patch on every asset. Each platform supports up to 10 rules.
Q: If I block a security patch, am I left exposed?
A: Not necessarily. Qualys-curated mitigations can reduce the risk while the patch is held back for testing and staging.
Q: Does the Patch Reliability Score change over time?
A: Yes. The score keeps updating as new feedback appears after release.
Q: How do I get access?
A: Every TruRisk Eliminate customer already has Patch Reliability. Patch Blocking Rules were added in release 4.2 for Windows, Linux, and Mac. To create them, you need the Manage Patch Blocking Rules permission, which the Patch Manager role has by default.