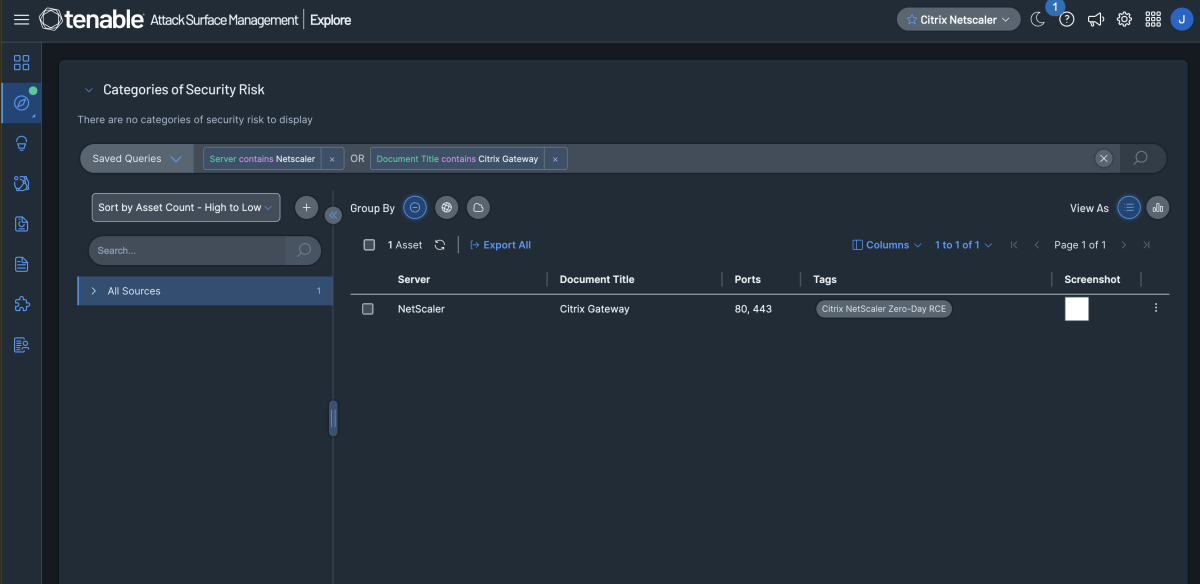
Overview
On September 27, 2026, Citrix disclosed eight new vulnerabilities affecting NetScaler ADC and NetScaler Gateway, including two critical remote code execution (RCE) vulnerabilities: CVE-2026-88771 and CVE-2026-88772. Both of these RCE vulnerabilities carry a critical CVSSv4 score of 9.5, and both have been confirmed as being actively exploited in the wild as zero-days prior to the vendor disclosure.
CVE-2026-88771 affects vulnerable NetScaler deployments in their default configuration, with no additional product features required. The vendor has also indicated that the attack complexity for exploiting CVE-2026-88771 is low, meaning reliable RCE is likely against all vulnerable NetScaler appliances regardless of their configuration. This is especially concerning due to the prevalence of NetScaler appliances.
CVE-2026-88772 is a memory corruption vulnerability and requires the DTLS feature to be enabled on the appliance. The vendor has indicated that the attack complexity is high, meaning achieving reliable exploitation may be more difficult for an attacker than that of CVE-2026-88771.
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) reports active exploitation is occurring globally, and added both CVE-2026-88771 and CVE-2026-88772 to its Known Exploited Vulnerabilities (KEV) catalog on September 27, 2026. Multiple CERTs worldwide have begun issuing alerts due to the critical nature of this situation.
The following table summarizes all eight vulnerabilities:
CVE
CVSSv4
Vulnerability
Exploitation confirmed
CVE-2026-88771
Improper input validation leading to RCE in a default configuration (CWE-20)
Yes ()
CVE-2026-88772
Memory overflow leading to RCE in a DTLS configuration (CWE-119)
Yes ()
CVE-2026-88773
HTTP request smuggling (CWE-444)
CVE-2026-88774
Policy bypass involving URL expressions (CWE-16)
CVE-2026-88775
Memory overflow in Gateway or AAA configuration (CWE-119)
CVE-2026-88776
Memory overflow in load balancer of type Oracle configuration (CWE-119)
CVE-2026-88777
Memory overflow in a LB/CS or CGNAT-LSN/NAT64 configuration (CWE-119)
CVE-2026-88778
Predictable TCP initial sequence numbers (CWE-342)
Mitigation guidance
The following vendor-supplied updates are available to remediate all eight vulnerabilities. Rapid7 strongly recommends updating affected NetScaler appliances on an emergency basis, outside of normal patching cycles, and investigating vulnerable appliances for signs of compromise.
- Citrix NetScaler ADC and Citrix NetScaler Gateway 14.1-73.37 and later releases.
Citrix NetScaler ADC and Citrix NetScaler Gateway 14.1-73.37 and later releases.
- Citrix NetScaler ADC and Citrix NetScaler Gateway 13.1-64.23 and later releases of 13.1.
Citrix NetScaler ADC and Citrix NetScaler Gateway 13.1-64.23 and later releases of 13.1.
- Citrix NetScaler ADC 14.1-FIPS 14.1-73.37 FIPS and later releases of 14.1-FIPS.
Citrix NetScaler ADC 14.1-FIPS 14.1-73.37 FIPS and later releases of 14.1-FIPS.
- Citrix NetScaler ADC 13.1-FIPS and 13.1-NDcPP 13.1.37.279 and later releases of 13.1-FIPS and 13.1-NDcPP.
Citrix NetScaler ADC 13.1-FIPS and 13.1-NDcPP 13.1.37.279 and later releases of 13.1-FIPS and 13.1-NDcPP.
For the latest mitigation guidance, please refer to the vendor .
Rapid7 customers
Exposure Command, InsightVM, and Nexpose
Exposure Command, InsightVM, and Nexpose customers can assess exposure to all the CVEs listed in this blog with authenticated vulnerability checks expected to be available in today’s (September 28) content release.
Intelligence Hub
Customers leveraging Rapid7’s Intelligence Hub can track the latest developments surrounding CVE-2026-88771 and CVE-2026-88772, including indicators of compromise (IOCs).
Updates
- September 28, 2026: Initial publication.
September 28, 2026: Initial publication.