This post is an exerpt from “A Bounty of Security,” originally posted on March 17, 2016 by Gregory Caswell on the Indeed Engineering Blog.
“A Bounty of Security”
“Do what’s best for the job seeker.” This has been Indeed’s guiding principle since the beginning. One way we put the job seeker first is by keeping their information safe and secure. We always consider the security of our systems as we develop the services that millions of people use every day. But someone will outsmart us. Hackers are always trying out new ways of bypassing security and gaining access to systems and information. Our challenge: to bring these security experts over to our side and benefit from their findings.
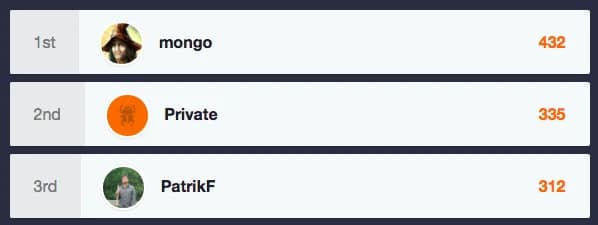
Our answer to this challenge is, well, money. Actually, money and fame. Indeed offers security testers a legitimate route to reporting their findings, and we award them for their time with cold, hard cash and recognition. Through our bug bounty program we have awarded over 300 submissions in the past year and a half, with payouts as high as $5,000 for the most severe bugs. Our most successful participants (looking at you, Angrylogic, Avlidienbrunn, and Mongo) have earned cash while building their reputations as highly regarded testers for Indeed.
Why create this program?
Prior to our bug bounty program, we occasionally received messages that sounded like blackmail. An anonymous person would contact us, insisting that we pay them, or they would publicly release the details of an unspecified, but totally serious, security bug. These individuals expected payment up front, with no guarantee that they even had a bug to expose. While we’re happy to compensate researchers for helping us improve our services, we didn’t want to encourage this coercive behavior. It felt wrong.
To solve the mutual distrust, we started using Bugcrowd.com as an impartial arbiter. On Bugcrowd, security researchers are more willing to provide evidence up front, giving us the chance to fairly assess the bug’s severity. Indeed can now provide rewards without abuse, and everyone lives happily ever after…
It has been a pleasure working with the Indeed team for the past year and a half. They are a group of extremely committed folks who are genuinely interested and invested in the responsible disclosure and bug bounty space. We look forward to continue working together. For the complete post, visit the Indeed Engineering Blog.